Modern applications are rarely a single process. A typical web product might combine an API server, a background worker, a relational database, a cache and a reverse proxy. Running each of these by hand, with the correct ports, volumes and environment variables, quickly becomes tedious and error-prone. docker compose exists to remove that friction. It lets you describe an entire multi-container application in one declarative file and then bring the whole system to life with a single command.
A concise definition
docker compose is a tool for defining and running multi-container applications. You write a YAML file, conventionally named compose.yaml or docker-compose.yml, which lists the services that make up your application together with the networks and volumes they share. Compose reads that file, works out the correct order of operations and instructs the Docker Engine to create everything accordingly.
The crucial idea is that the file is declarative: you state the desired end result rather than the sequence of steps required to reach it. If the running system drifts from the description, running the command again reconciles the two.
Why Compose matters
Before Compose became commonplace, teams documented their local set-up in lengthy README files filled with docker run commands. Those instructions aged badly and differed subtly from one laptop to the next. Compose replaced the prose with a machine-readable contract that can be versioned alongside the source code. The practical benefits are considerable:
- Reproducibility. Every developer, and every CI job, starts from an identical definition.
- Speed of onboarding. A newcomer clones the repository, runs
docker compose upand has a working stack within minutes. - Isolation. Each project gets its own network and namespace, so two applications using PostgreSQL on port 5432 do not collide.
- Readability. The Compose file doubles as living documentation of the architecture.
The anatomy of a Compose file
A Compose file is built from a small number of top-level elements. The most important is services; the others are optional and are added only when needed.
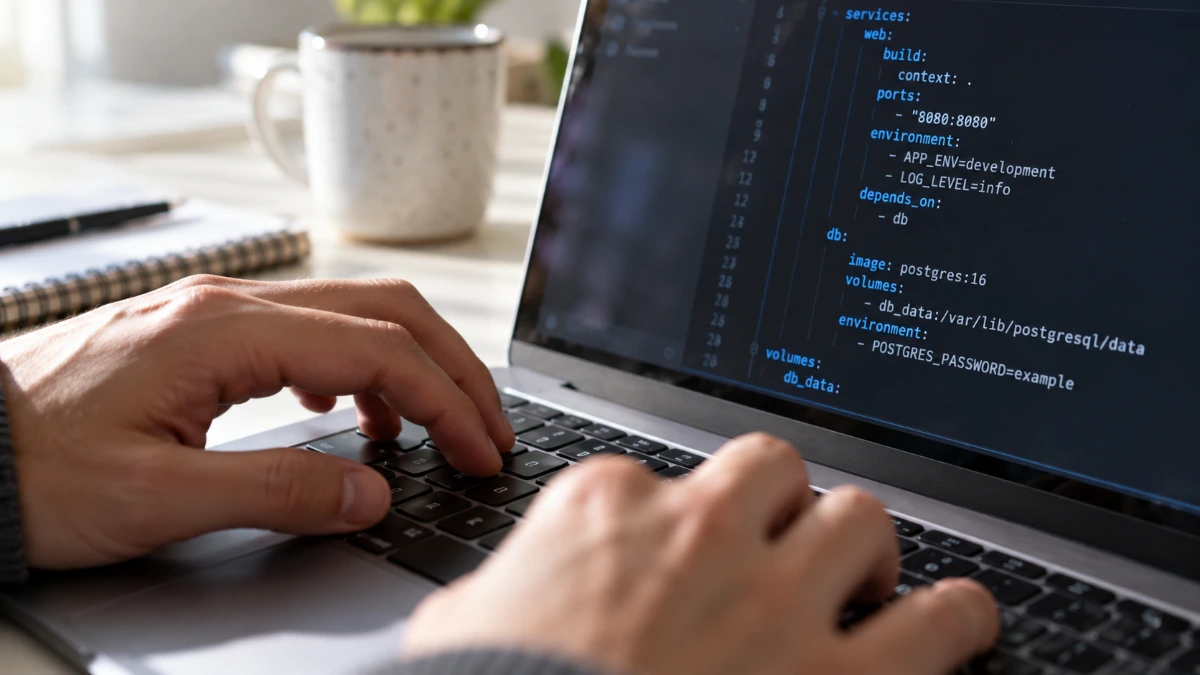
services:
  web:
    build: .
    ports:
      - "8000:8000"
    depends_on:
      - db
  db:
    image: postgres:17
    environment:
      POSTGRES_PASSWORD: example
    volumes:
      - db-data:/var/lib/postgresql/data

volumes:
  db-data:
Here two services are declared. The web service is built from a local Dockerfile, while db uses an official image. A named volume preserves the database files across restarts, and Compose automatically places both containers on a private network where each can reach the other by its service name.
Compose, the CLI and the Specification
It is worth distinguishing three related ideas. The Compose Specification is the open standard that defines what a valid Compose file may contain. The Compose CLI is the tool that implements that standard; today it ships as a plug-in invoked as docker compose (with a space). Finally, the legacy Python program docker-compose (with a hyphen) belongs to the original 1.x generation and is no longer maintained.
Where Compose fits — and where it does not
Compose excels on a single host: local development, automated testing, demonstrations, small internal tools and modest production deployments on one server. It is deliberately not a cluster scheduler. When an application must span many machines, heal itself after node failure or autoscale across a fleet, an orchestrator such as Kubernetes is the more appropriate choice. Many teams therefore use Compose for development and a different platform for large-scale production, keeping the two in step through shared images.
Configuration as an operational contract
A Compose file is most valuable when treated as an explicit contract between application developers and the people responsible for its operation. Service names establish a vocabulary, networks establish communication boundaries, and volumes establish the ownership of persistent state. Review these decisions alongside application code rather than delegating them to undocumented workstation conventions.
Reproducibility has limits: host architecture, mutable image tags and external infrastructure can still change behaviour. Pin important dependencies, retain migration procedures and distinguish deterministic application configuration from the environmental assumptions it cannot enforce.
How a docker compose project fits together
A useful way to understand docker compose is to follow a request through a small application. A browser connects to a published port on your computer. Docker forwards that connection into a web container. The web application then contacts a database by its service name on the project network. The database writes durable records to a named volume. Each part has a separate responsibility, while the Compose file describes how the parts cooperate. You can inspect the whole arrangement without remembering a long sequence of individual container commands or asking a teammate which network they created yesterday.
The project is also an important boundary. Compose groups resources using a project name, which is normally derived from the project directory unless you override it. Two developers can therefore run similar applications without intentionally sharing containers or networks. When you use the project flag, keep it consistent across startup, inspection and shutdown commands. Otherwise you may inspect a different project and mistakenly think that your containers have disappeared. Published host ports still need to be unique, even when the projects themselves have different names.
Understanding configuration and container state
Your Compose file describes the desired application arrangement, but the running containers also have state. Editing an environment value in YAML does not rewrite the environment inside an existing process. Run the appropriate Compose startup operation to reconcile configuration changes with the running application. Rebuilding an image and recreating a container are related but different operations: a source change copied during an image build needs a new build, while a configuration change may only require recreation. Knowing which layer changed saves time and avoids repeatedly rebuilding an image that was already correct.
A container is replaceable, so important application data should live outside its writable layer. Named volumes are a common choice for databases; bind mounts are useful when a developer needs live access to local source files. Neither arrangement automatically gives you a backup. Decide which information must survive replacement, where it is stored and how it can be restored. A project that starts successfully but loses its database during routine cleanup is not yet a dependable development environment. Practise recovery with disposable data before trusting the workflow with valuable records.
A practical learning sequence
Start with one web service whose behaviour you already understand. Run docker compose config to validate the model, then start the service and inspect its status and logs. Next add a database, connect through the database service name and verify a complete request. Only after that should you introduce profiles, additional configuration files or resource tuning. This sequence gives every new option a reason to exist. When something breaks, you can compare the result with the last working step instead of investigating a large unfamiliar configuration all at once.
For team use, commit the Compose file alongside the application and provide an example of the required configuration values. Keep real passwords and access tokens outside the repository. Document the command used to start the project, the local address of the application and the procedure for running tests. A short setup note is more useful than an unexplained collection of optional services. Ask a teammate to start from a clean checkout: their first attempt often reveals an undeclared dependency that your own computer has silently supplied for months.
Frequently asked questions
Is docker compose a replacement for Docker Engine?
No. Compose describes and coordinates containers through a Docker runtime. You still need a working engine and permission to access it. A successful version command confirms that the Compose client exists, while docker info helps confirm that the selected engine is reachable.
Can I use docker compose for only one container?
Yes. A single service can benefit from a saved port mapping, environment configuration and volume declaration. You can add related services later without changing the basic project workflow. The value comes from repeatable configuration, rather than a minimum container count.
Does stopping docker compose remove database data?
Stopping containers does not normally remove named volumes. However, explicitly removing volumes can destroy their contents, and data kept only in a container layer can disappear when that container is replaced. Always identify the storage location before running cleanup commands.
Why can my app not reach its database through localhost?
Inside a container, localhost normally refers to that same container. Another service on a shared Compose network should usually be reached through its service name and internal port. Your browser, by contrast, connects through a published host port.
Conclusion
Docker compose turns an application's services, networks and storage into a repeatable project. Learn the relationships between those resources before collecting advanced options. Validate the file, inspect running services and confirm that data survives the lifecycle operations you expect to use. With those habits, the same configuration can help an individual developer get started and give a team a shared foundation for testing, troubleshooting and maintaining its application. Keep this working baseline documented so teammates can repeat the same workflow.